Download the PHP package laravel/vet without Composer
On this page you can find all versions of the php package laravel/vet. It is possible to download/install these versions without Composer. Possible dependencies are resolved automatically.
FAQ
Example:

In general, it is recommended to use always a project to download your libraries. In an application normally there is more than one library needed.

- Some hosting areas are not accessible by a terminal or SSH. Then it is not possible to use Composer.
- To use Composer is sometimes complicated. Especially for beginners.
- Composer needs much resources. Sometimes they are not available on a simple webspace.
- If you are using private repositories you don't need to share your credentials. You can set up everything on our site and then you provide a simple download link to your team member.
- Simplify your Composer build process. Use our own command line tool to download the vendor folder as binary. This makes your build process faster and you don't need to expose your credentials for private repositories.
Informations about the package vet
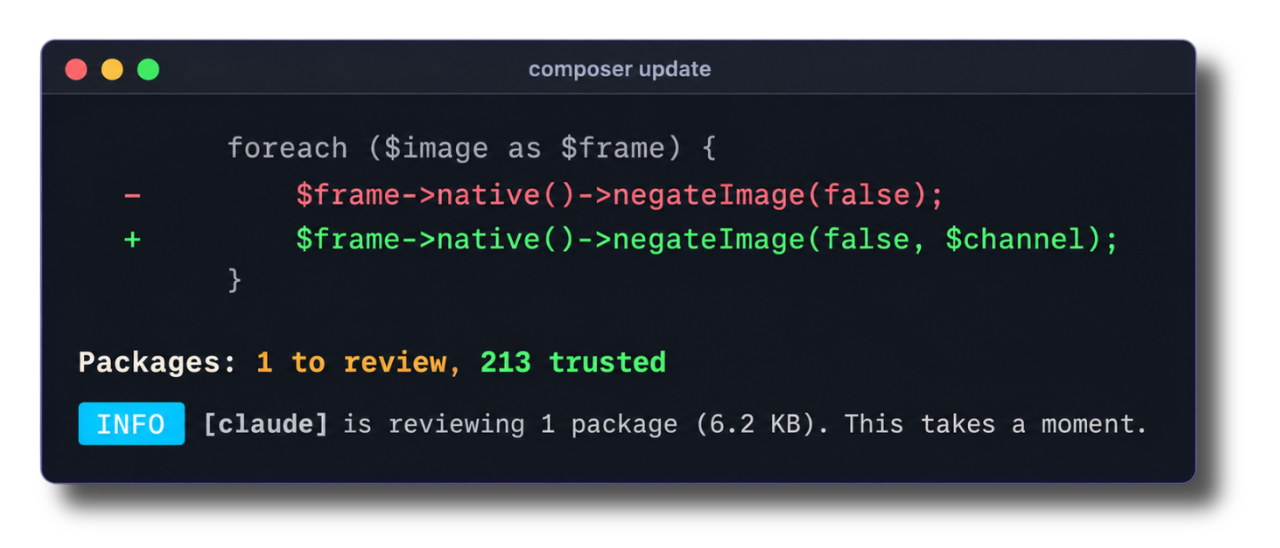
[!WARNING] Laravel Vet is a work in progress, and has no tagged release yet. Use it at your own risk.
Laravel Vet is a dependency audit for PHP. It shows you the code that composer update is about to write into your vendor/ directory, and records the packages you trust in a vet.json file.
If you know cargo vet from the Rust world, this is the same idea for Composer. If you don't, here is the whole idea: every update brings new code into your project that nobody on your team has read. Vet shows you that code, one package at a time, before it lands. Once you trust a package, vet remembers it, so the next update only asks about what changed.
You don't have to read it all yourself. Vet hands each change to the coding agent already on your machine, such as Claude Code, Codex or Gemini, and the agent reads it for you and reports back: PASS, or FAIL with the file and the reason. You read the fails, press enter on the rest, and get on with your day.
Vet works with any PHP project. Laravel, Symfony, WordPress, or plain PHP: if you have a composer.json, you can use it. It ships as a Composer plugin, so it runs after every composer install and before every composer update writes anything. There is no step to add.
You read the changes, or you let your agent read them, and vet writes your decision down. Your build then holds you to it: a package that nobody has trusted fails the build until someone reads it.
Installation
Requires PHP 8.4+.
You can install Laravel Vet via Composer:
Composer asks whether to allow the plugin the first time. Answer yes, and vet runs on every install and update from then on. You can also run it yourself with the ./vendor/bin/vet script that is included with the package:
Vet has one command. It audits what vendor/ holds, and when you run it in a terminal, it asks which of the untrusted packages you trust. You can read the changes yourself, or ask your coding agent to read them first. Until vet.json exists, vet has no earlier version to compare an update against, so the first step is to record the packages you trust today.
Recording Your Baseline
The --init option records every package that vendor/ holds today, and writes vet.json for the first time. The --fresh option deletes vet.json first, then does the same, so you start from an empty trust file:
The --init option trusts the bytes that are already on your disk, and nothing else. When composer.lock asks for a version that vendor/ does not hold yet, vet leaves that version alone and asks you to read it:
Auditing Your Dependencies
Once the trust file exists, vet tells you where you stand. It reads every installed package, compares it against your entries, and names the packages that have none:
Vet exits with a non-zero status when a package is not trusted, which is what makes it useful in a build. Without a terminal, in your CI or inside the Composer plugin, the report is all that vet writes.
Until vet.json exists, vet audits nothing and asks no question. It names the command that starts the trust file, and exits with a non-zero status:
Picking What to Trust
In a terminal, vet follows the report with a question. Every package that you do not trust yet appears in the list. Press the space bar to pick a package, ctrl+a to pick every package, and enter to record the ones that you picked. The changes of each package sit in the report above the list, so you read first and pick second:
The run exits with a non-zero status until you trust every package. A package you skip fails the run, in the same way it fails your build.
Above ten packages, the report lists each package with the count of its changed files and shows no change. A change that runs past forty lines stops there, and vet <package> shows the rest. Vet prints one dot for each archive that it downloads, and one for each package that the agent finishes.
Auditing a Single Package
You may audit one package, or a few, by passing their names. Vet shows you the package, and records nothing:
When the trust file already trusts the installed version, the report stays local. When the trust file holds an earlier version, vet fetches that version from Packagist and shows you the changes. The --from and --to options compare any two versions:
Reading the Changes
Vet sorts the changed files into four buckets, and shows you the ones that can hurt you first:
| Bucket | What it holds |
|---|---|
install-time manifest |
The composer.json of the package, which can add a script that runs at install time |
opaque artifact |
Bytes that nobody can read, such as a .phar or a compiled library |
runtime source |
The source that your application autoloads and executes |
inert |
Everything else, such as tests, documentation and images |
Handing a Review to Your Agent
Reading every change by hand takes time, and most of the time you won't want to. In a terminal, the first question offers the coding agent already on your machine. Pick it, and vet hands the changes of each package to the agent, and prints the result next to the package. You still make the call. The agent reads, and you decide:
A result is one of four. PASS means the agent read every file and found no attack. FAIL comes with one line for each file the agent names. WARN means the rest of the reading is yours: the agent did not read every file, or its answer did not arrive. When a file is too big for the prompt, or holds no text, such as a .phar, WARN names that file, the reason and its size. SKIP means vet sent nothing, because no file changed or vet cannot read the files of the package.
In a terminal, each result sits on its row of the list, and vet picks every PASS row for you before you read it. One enter records those packages, and you read each FAIL and WARN before you decide:
Before the agent reads, vet asks which model it uses. Pick one from the list, type a name, or press enter to keep the default model of the agent:
The --model option gives the answer without the question:
The agent runs only when you ask for it. The Composer plugin never asks, and a result writes nothing to vet.json until you answer the question, so the decision stays yours.
Vet prints the count and the size of the prompts before the first one leaves your machine, so you can stop it there.
How the Agent Reads
Vet looks for claude, then codex, then gemini on your PATH, and gives it the prompt on standard input. The VET_AGENT_BINARY environment variable names a different one.
Vet turns the tools of the agent off and asks for one JSON object back, so the agent reads the changes and does nothing else. The changes stand inside a marker that carries a token of the run, and vet checks every file the answer names against the files it sent.
A package with no entry in your trust file has no earlier version to compare against. Vet sends the whole package instead, because that is the package you know least.
The Trust File
The trust file lives in vet.json, at the root of your project, next to composer.json. You should commit it. It holds one entry for each package: the version you read, and the hash of the files you read:
The hash covers every file of the package. When a package ships the same version with different bytes, the entry stops trusting it, and vet asks you to read the difference.
Continuous Integration
Your build audits your dependencies the moment it installs them. Vet ships a Composer plugin, and the plugin runs the audit after every composer install, and again before composer update writes anything into vendor/. There is no step to add.
The --no-plugins option of Composer runs one command without the plugin, so the update writes into vendor/ and nobody reads it until you run vet:
Configuration
Vet reads three environment variables:
VET_AGENT_BINARY names the coding agent that vet runs. VET_GITHUB_TOKEN authenticates the archives that vet downloads from GitHub, and vet falls back to GITHUB_TOKEN, to GH_TOKEN, and to your Composer authentication file. VET_CACHE_DIR holds the archives that vet has already downloaded, and defaults to vet inside $XDG_CACHE_HOME, or inside $HOME/.cache.
Pass the --no-cache option to download an archive again instead of reading the cached one:
Contributing
Thank you for considering contributing to Laravel! The contribution guide can be found in the Laravel documentation.
Code of Conduct
In order to ensure that the Laravel community is welcoming to all, please review and abide by the Code of Conduct.
Security Vulnerabilities
Please review our security policy on how to report security vulnerabilities.
License
Laravel Vet is open-sourced software licensed under the MIT license.
All versions of vet with dependencies

composer-plugin-api Version ^2.0
ext-dom Version *
ext-mbstring Version *
ext-openssl Version *
ext-phar Version *
ext-zip Version *