Libraries tagged by hash code
nogrod/tyre24-seller-php-sdk
671 Downloads
## API Versioning We're constantly updating and improving the API, and while we try to ensure backwards compatibility, there's always a chance that we'll introduce a change that affects the way your app works. To get around any problems that this might cause, we recommend that you include the Accept header with every API request that you make. This header enables you to target your request to a particular version of the API. It looks like this in HTTP: ```text Accept: application/vnd.saitowag.api+json;version={version_number} ``` Normally, you set the value of the placeholder to the current version of the API. But if you're troubleshooting your app, and you know that an older version of the API works perfectly, say version 1.0, you'd substitute 1.0 for the placeholder value. The API then handles the request as if it were for version 1.0, and your app goes back to working properly. ### Example of an error with invalid `ACCEPT` header. The `HTTP status code` in case of an invalid `ACCEPT` header will be `400 Bad Request` and the following response will be returned. ```json { "data": [ { "error_code": "ERR_ACCEPT_HEADER_NOT_VALID", "error_message": "Accept header is not valid or not set." } ] } ``` ### Unexpected Error If an unexpected error occours, a so called Error General will be returned. The `HTTP status code` in case of an invalid `ACCEPT` header will be `500` and the following response will be returned. ```json { "data": [ { "error_code": "ERR_GENERAL", "error_message": "An unexpected error has occurred. If this problem persists, please contact our support." } ] } ``` ### Invalid Endpoint Error Any call to a non-existing API endpoint (i.e. wrong route) will return a response with `HTTP status code` `404` and the following response body: ```json { "data": [ { "error_code": "ERR_GENERAL_INVALID_ENDPOINT", "error_message": "The requested endpoint does not exist." } ] } ``` Please, note that this error is returned also when a request parameter, part of a valid route, is not well formed. For example, a call to a route that contains a wrong order id (i.e. it does not meet the accepted order id pattern - e.g. 123456789PAC instead of PAC123456789) will return the error just mentioned, as the route is considered as badly formed. In conclusion, please pay special attention to all those routes that have request parameters with specific pattern requirements. ### Shipping Method IDs These ids may not be available in all the countries. | ID | Name | | --- | --- | | 1 | Standard `Standard` | | 2 | Self-collection `Selbstabholung` | | 3 | Express morning (truck) `Express-Morgen (LKW)` | | 4 | Express Today (Truck) `Express-Heute (LKW)` | | 5 | Express morning (package forwarding) `Express-Morgen (Packet Spedition)` | | 7 | Express-now | ### Payment Method IDs These ids may not be available in all the countries. | ID | Name | | --- | --- | | 1 | SEPA Direct Debit `SEPA-Lastschrift` | | 2 | Prepayment `Vorkasse` | | 3 | Cash on delivery `Nachnahme` | | 4 | PayPal/Credit Card `PayPal/Kreditkarte` | | 5 | open payment method `offene Zahlungsart` | | 7 | Invoice(8 days payment term) `Rechnung(8 Tage Zahlungsziel)` | | 8 | open payment method (SEPA) `offene Zahlungsart (SEPA)` | ## Query String Filters Query String Filters | Operator | Full Name | Description | Example | | ------ | ------ | ------ | ------ | | eq | Equal | Used to narrow down the result of a query to some specific value, for specified field. It adds the "**=**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=eq;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} = 11` | integer: `{url}?filter[id]=eq;21`float: `{url}?filter[average]=eq;3.7`string: `{url}?filter[free_text]=eq;apple`Date: `{url}?filter[birthday]=eq;2020-06-03`DateTime: `{url}?filter[created_at]=eq;2020-06-03 14:32:32`boolean: `{url}?filter[is_active]=eq;1` | | neq | Not equal | Used to exclude the value from a query result. It adds the "****" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=neq;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} 11` | integer: `{url}?filter[id]=neq;21`float: `{url}?filter[average]=neq;3.7`string: `{url}?filter[free_text]=neq;apple`Date: `{url}?filter[birthday]=neq;2020-06-03`DateTime: `{url}?filter[created_at]=neq;2020-06-03 14:32:32`boolean: `{url}?filter[is_active]=neq;1` | | gt | Greater than | Used to reduce fetched values to those greater than the one provided in a query string. It adds the "**>**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=gt;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} > 11` | integer: `{url}?filter[id]=gt;21`float: `{url}?filter[average]=gt;3.7`Date: `{url}?filter[birthday]=gt;2020-06-03`DateTime: `{url}?filter[created_at]=gt;2020-06-03 14:32:32` | | gte | Greater than or equal | Used to reduce fetched values to those greater than or equal to the one provided in a query string. It adds the "**>=**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=gte;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} >= 11` | integer: `{url}?filter[id]=gte;21`float: `{url}?filter[average]=gte;3.7`Date: `{url}?filter[birthday]=gte;2020-06-03`DateTime: `{url}?filter[created_at]=gte;2020-06-03 14:32:32` | | lt | Less than | Used to reduce fetched values to those less than provided in a query string. It adds the "**
nogrod/tyre24-common-php-sdk
667 Downloads
## API Versioning We're constantly updating and improving the API, and while we try to ensure backwards compatibility, there's always a chance that we'll introduce a change that affects the way your app works. To get around any problems that this might cause, we recommend that you include the Accept header with every API request that you make. This header enables you to target your request to a particular version of the API. It looks like this in HTTP: ```text Accept: application/vnd.saitowag.api+json;version={version_number} ``` Normally, you set the value of the placeholder to the current version of the API. But if you're troubleshooting your app, and you know that an older version of the API works perfectly, say version 1.0, you'd substitute 1.0 for the placeholder value. The API then handles the request as if it were for version 1.0, and your app goes back to working properly. ### Example of an error with invalid `ACCEPT` header. The `HTTP status code` in case of an invalid `ACCEPT` header will be `400 Bad Request` and the following response will be returned. ```json { "data": [ { "error_code": "ERR_ACCEPT_HEADER_NOT_VALID", "error_message": "Accept header is not valid or not set." } ] } ``` ### Unexpected Error If an unexpected error occours, a so called Error General will be returned. The `HTTP status code` in case of an invalid `ACCEPT` header will be `500` and the following response will be returned. ```json { "data": [ { "error_code": "ERR_GENERAL", "error_message": "An unexpected error has occurred. If this problem persists, please contact our support." } ] } ``` ### Invalid Endpoint Error Any call to a non-existing API endpoint (i.e. wrong route) will return a response with `HTTP status code` `404` and the following response body: ```json { "data": [ { "error_code": "ERR_GENERAL_INVALID_ENDPOINT", "error_message": "The requested endpoint does not exist." } ] } ``` Please, note that this error is returned also when a request parameter, part of a valid route, is not well formed. For example, a call to a route that contains a wrong order id (i.e. it does not meet the accepted order id pattern - e.g. 123456789PAC instead of PAC123456789) will return the error just mentioned, as the route is considered as badly formed. In conclusion, please pay special attention to all those routes that have request parameters with specific pattern requirements. ### Shipping Method IDs These ids may not be available in all the countries. | ID | Name | | --- | --- | | 1 | Standard `Standard` | | 2 | Self-collection `Selbstabholung` | | 3 | Express morning (truck) `Express-Morgen (LKW)` | | 4 | Express Today (Truck) `Express-Heute (LKW)` | | 5 | Express morning (package forwarding) `Express-Morgen (Packet Spedition)` | | 7 | Express-now | ### Payment Method IDs These ids may not be available in all the countries. | ID | Name | | --- | --- | | 1 | SEPA Direct Debit `SEPA-Lastschrift` | | 2 | Prepayment `Vorkasse` | | 3 | Cash on delivery `Nachnahme` | | 4 | PayPal/Credit Card `PayPal/Kreditkarte` | | 5 | open payment method `offene Zahlungsart` | | 7 | Invoice(8 days payment term) `Rechnung(8 Tage Zahlungsziel)` | | 8 | open payment method (SEPA) `offene Zahlungsart (SEPA)` | ## Query String Filters Query String Filters | Operator | Full Name | Description | Example | | ------ | ------ | ------ | ------ | | eq | Equal | Used to narrow down the result of a query to some specific value, for specified field. It adds the "**=**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=eq;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} = 11` | integer: `{url}?filter[id]=eq;21`float: `{url}?filter[average]=eq;3.7`string: `{url}?filter[free_text]=eq;apple`Date: `{url}?filter[birthday]=eq;2020-06-03`DateTime: `{url}?filter[created_at]=eq;2020-06-03 14:32:32`boolean: `{url}?filter[is_active]=eq;1` | | neq | Not equal | Used to exclude the value from a query result. It adds the "****" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=neq;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} 11` | integer: `{url}?filter[id]=neq;21`float: `{url}?filter[average]=neq;3.7`string: `{url}?filter[free_text]=neq;apple`Date: `{url}?filter[birthday]=neq;2020-06-03`DateTime: `{url}?filter[created_at]=neq;2020-06-03 14:32:32`boolean: `{url}?filter[is_active]=neq;1` | | gt | Greater than | Used to reduce fetched values to those greater than the one provided in a query string. It adds the "**>**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=gt;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} > 11` | integer: `{url}?filter[id]=gt;21`float: `{url}?filter[average]=gt;3.7`Date: `{url}?filter[birthday]=gt;2020-06-03`DateTime: `{url}?filter[created_at]=gt;2020-06-03 14:32:32` | | gte | Greater than or equal | Used to reduce fetched values to those greater than or equal to the one provided in a query string. It adds the "**>=**" symbol to the SQL query. Eg. `{url}?filter[{alias_name}]=gte;11` will result in the following sql: `SELECT {field_name} AS {alias_name} FROM {table_name} WHERE {alias_name} >= 11` | integer: `{url}?filter[id]=gte;21`float: `{url}?filter[average]=gte;3.7`Date: `{url}?filter[birthday]=gte;2020-06-03`DateTime: `{url}?filter[created_at]=gte;2020-06-03 14:32:32` | | lt | Less than | Used to reduce fetched values to those less than provided in a query string. It adds the "**
briqpay/php-sdk
12159 Downloads
This is the API documentation for Briqpay. You can find out more about us and our offering at our website [https://briqpay.com](https://briqpay.com) In order to get credentials to the playgrund API Please register at [https://app.briqpay.com](https://app.briqpay.com) # Introduction Briqpay Checkout is an inline checkout solution for your b2b ecommerce. Briqpay Checkout gives you the flexibility of controlling your payment methods and credit rules while optimizing the UX for your customers # SDKs Briqpay offers standard SDKs to PHP and .NET based on these swagger definitions. You can download them respively or use our swagger defintitions to codegen your own versions. #### For .NET `` Install-Package Briqpay `` #### For PHP `` composer require briqpay/php-sdk `` # Standard use-case As a first step of integration you will need to create a checkout session. \n\nIn this session you provide Briqpay with the basic information necessary. In the response from briqpay you will recieve a htmlsnippet that is to be inserted into your frontend. The snippet provided by briqpay will render an iframe where the user will complete the purchase. Once completed, briqpay will redirect the customer to a confirmation page that you have defined. 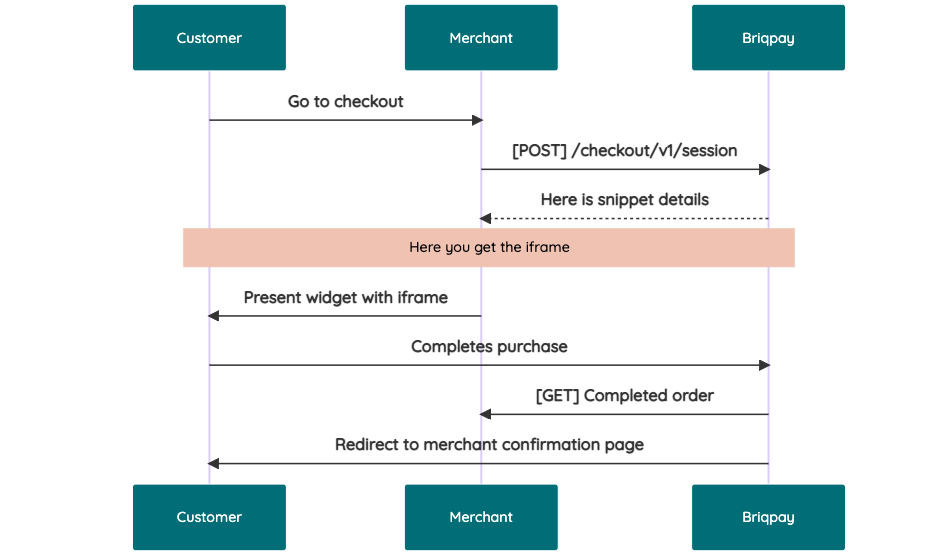 # JavaScript SDK The first step of integration is to add our JS to your site just before closing the ```` tag. This ensures that our JS library is avaliable to load the checkout. ```` Briqpay offers a few methods avaliable through our Javascript SDK. The library is added by our iframe and is avalable on ``window._briqpay`` If you offer the posibility to update the cart or order amonts on the checkout page, the JS library will help you. If your store charges the customer different costs and fees depening on their shipping location, you can listen to the ``addressupdate``event in order to re-calculate the total cost. ```javascript window._briqpay.subscribe('addressupdate', function (data) { console.log(data) }) ``` If your frontend needs to perform an action whe the signup has completed, listen to the ``signup_finalized`` event. ```javascript window._briqpay.subscribe('signup_finalized', function (status) { // redirect or handle status 'success' / 'failure' }) ``` If you allow customers to change the total cart value, you can utilise the JS library to suspend the iframe while you perform a backen update call towards our services. As described below: 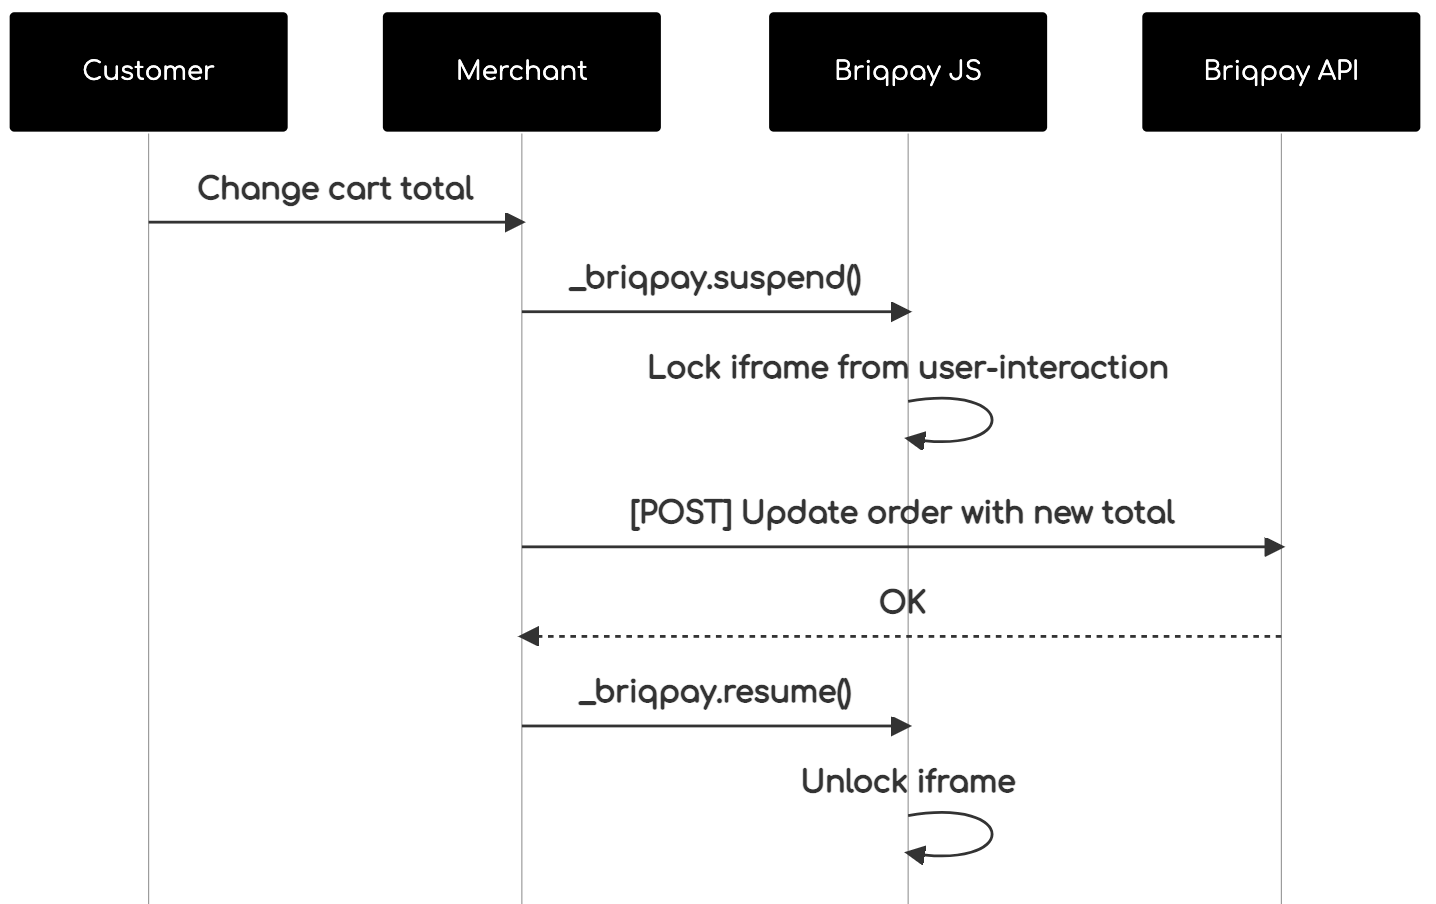 The iframe will auto-resume after 7 seconds if you dont call ``_briqpay.resume()`` before # Test Data In order to verify your integration you will neeed to use test data towards our credit engine. ## Company identication numbers * 1111111111 - To recieve a high credit scoring company ( 100 in rating) * 2222222222 - To test the enviournment with a bad credit scoring company (10 in rating) ## Card details In our playground setup your account is by default setup with a Stripe integration. In order to test out the card form you can use the below card numbers: * 4000002500003155 - To mock 3ds authentication window * 4000000000000069 Charge is declined with an expired_card code. You can use any valid expiry and CVC code # Authentication Briqpay utilizes JWT in order to authenticate calls to our platform. Authentication tokens expire after 48 hours, and at that point you can generate a new token for the given resource using the ``/auth`` endpoint. - Basic Auth - only used on the auth endpoint in order to get the Bearer Token - JWT Bearer Token - All calls towards the API utlizes this method"
phuture/coherence
7 Downloads
A coherent collection of utility helpers for PHP.
codeitnowin/curlrequestit
47 Downloads
Light weight curl request library by http://www.codeitnow.in, It has setters and getters to make easy to use. You can use Curl Request with any framework like Symfony, Laravel, CackPHP, CodeIgniter, Yii etc. This is alternate of Guzzle and other libraries.
serger/cake-utility
225 Downloads
CakePHP 3.x Utility classes such as Inflector, String, and Hash without Cake/Core dependency
cic/wp-webpack-assets
750 Downloads
Load assets from webpack built asset manifest. Requires something like: https://www.npmjs.com/package/webpack-php-manifest
tyhpdef/php
23 Downloads
Tyhp type definitions for always-present PHP built-ins (8.2+) — Core, date, filter, hash, json, libxml, pcre, random, Reflection, SPL, standard. Version-specific APIs are gated via declare(php=…) / #[\Tyhp\Php].
gamitg/yii2-ag-scheduling
176 Downloads
This extension is a variation of the yii2-scheduling extension of Yii2. It has simply the same code with a few modification with supported to PHP8. Thanks to 'yii2-scheduling (Developed by: omnilight) extension'.
fwartner/maps
726 Downloads
A codeigniter library that has been modified a bit so that it's laravel friendly forked by fwartner
wpcompatibility/wp-compatibility
31 Downloads
WPCompatibility has a collection of PHPCS sniffs which will tell you if your plugin/theme code is compatible with a specific wordpress version
sameer-shelavale/multi-captcha
169 Downloads
Multiple(7) types of CAPTCHA in one package. Supports Gif captcha( Animated Gif captcha), Image Captcha( User has to type SOME OR ALL part of code displayed in the image), HoneyPot captcha(It simply adds an empty field asking users to leave it blank. Bots fill it up.), ASCII captcha(It displays the CAPTCHA text as ASCII Art. User has to type SOME OR ALL part of the code.), Math captcha( It asks user to solve simple mathematical expressions.), Recaptcha(Google Recaptcha) and NoCaptcha(Google ReCaptcha v2.0). This package also has captcha refresh feature.
privacy-ci/laravel
7 Downloads
Find where personal data lives in your Laravel app, classify it in policy-as-code, and fail CI when new user-linked storage has no policy.
oscarricardosan/cache_object
1057 Downloads
Small package for handling cache in code block and not having to use session and avoid 'array_has' or the like.
crimsonkissaki/mockmaker
44 Downloads
Whether you call them doubles, stubs, mocks, partials, fakes, or something else there are times when a mocking library such as PHPUnit's mockBuilder, Mockery, Prophecy, etc. just doesn't do exactly what you need or want. Sometimes you just need a concrete class implementation to run through the unit test wringer or a full end to end functional unit test suite. MockMaker aims to simplify the process of generating concrete fake ORM entity objects. Flexible and extendable, the generated seed code can be altered to suit your particular project with relative ease. That means after the initial setup you can re-run MockMaker for any new entities that get added in or update existing entities that change with little to no fuss. What's more, once MockMaker has made your files it's done; you don't have to include it in your code base and can use the generated files like any other project class.