Libraries tagged by php http code
konfig/snaptrade-php-7-sdk
759 Downloads
Connect brokerage accounts to your app for live positions and trading. ## Rate limiting Two limits apply to requests signed with your `clientId`. The stricter one wins, and exceeding either returns `429 Too Many Requests`. - **Customer-level** — 250 requests/minute by default, scoped to your `clientId` and applied across all endpoints. Reported in `X-RateLimit-Limit`, `X-RateLimit-Remaining` and `X-RateLimit-Reset`. - **Account-level** — 10 requests/minute per account, scoped to (`clientId`, `accountId`). All covered operations for one account draw on the same bucket — reading balances and reading positions share it — and enforcement does not depend on the HTTP method, so updating an account consumes the same bucket as reading it. Only enforced for Personal users, and only for integrations it has been rolled out to — it is not yet in force for every Personal integration. It also does not apply on every operation that documents a 429 below. Where it applies it is reported in `X-RateLimit-Account-Limit`, `X-RateLimit-Account-Remaining` and `X-RateLimit-Account-Reset`. Do not read the absence of those headers as proof the limit is off — some configurations omit the rate limit headers while still enforcing the limit, so header absence tells you nothing about your allowance. On a 429, `X-RateLimit-Remaining: 0` means you hit the customer-level limit and `X-RateLimit-Account-Remaining: 0` means the account-level one. Wait for the corresponding `*-Reset` value (seconds) before retrying, or fall back to exponential backoff with jitter. Not every 429 is explained by those headers. A separate per-authenticated-user limit, reported in no `X-RateLimit-*` header, covers OAuth-authenticated requests and signed requests in configurations where the customer-level limit is not in effect — on the operations that use the default throttles. A few operations override those and are governed by the customer-level limit alone. The two do not stack: a signed request governed by the customer-level limit above is not additionally subject to the per-user one. If a 429 arrives with no header at zero — or with no `X-RateLimit-*` headers at all — honour `Retry-After` and back off. Treat the remaining counts as a hint, not a guarantee that the next request will succeed. Because the customer-level limit applies everywhere, any signed request can return 429. **OAuth-authenticated requests are an exception.** They are not subject to the customer-level limit and do not receive `X-RateLimit-Limit`, `X-RateLimit-Remaining` or `X-RateLimit-Reset` — do not wait on those headers or design around a customer-level allowance on this path. The account-level limit still applies to them on the account-data endpoints above, reported in the `X-RateLimit-Account-*` headers. On operations using the default throttles the per-user limit above applies to them as well, so an OAuth request can be rejected while the account headers still show capacity; on the few operations that override those throttles, OAuth callers have no per-user ceiling at all. Drive retries from `Retry-After` and exponential backoff with jitter rather than from the headers. See https://docs.snaptrade.com/docs/ratelimiting.
hengebytes/soap-core-async-bundle
402 Downloads
Symfony bundle for using http client as soap async client
briqpay/php-sdk
12246 Downloads
This is the API documentation for Briqpay. You can find out more about us and our offering at our website [https://briqpay.com](https://briqpay.com) In order to get credentials to the playgrund API Please register at [https://app.briqpay.com](https://app.briqpay.com) # Introduction Briqpay Checkout is an inline checkout solution for your b2b ecommerce. Briqpay Checkout gives you the flexibility of controlling your payment methods and credit rules while optimizing the UX for your customers # SDKs Briqpay offers standard SDKs to PHP and .NET based on these swagger definitions. You can download them respively or use our swagger defintitions to codegen your own versions. #### For .NET `` Install-Package Briqpay `` #### For PHP `` composer require briqpay/php-sdk `` # Standard use-case As a first step of integration you will need to create a checkout session. \n\nIn this session you provide Briqpay with the basic information necessary. In the response from briqpay you will recieve a htmlsnippet that is to be inserted into your frontend. The snippet provided by briqpay will render an iframe where the user will complete the purchase. Once completed, briqpay will redirect the customer to a confirmation page that you have defined. 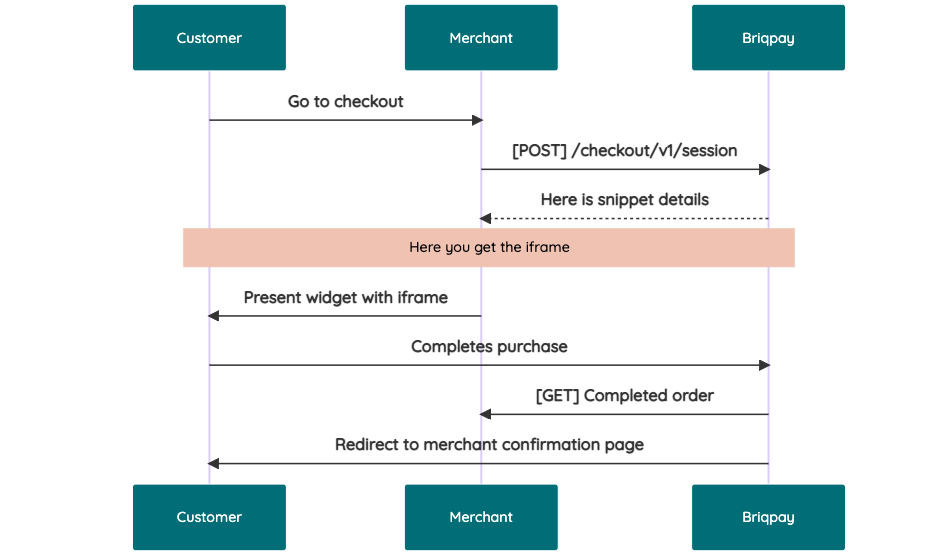 # JavaScript SDK The first step of integration is to add our JS to your site just before closing the ```` tag. This ensures that our JS library is avaliable to load the checkout. ```` Briqpay offers a few methods avaliable through our Javascript SDK. The library is added by our iframe and is avalable on ``window._briqpay`` If you offer the posibility to update the cart or order amonts on the checkout page, the JS library will help you. If your store charges the customer different costs and fees depening on their shipping location, you can listen to the ``addressupdate``event in order to re-calculate the total cost. ```javascript window._briqpay.subscribe('addressupdate', function (data) { console.log(data) }) ``` If your frontend needs to perform an action whe the signup has completed, listen to the ``signup_finalized`` event. ```javascript window._briqpay.subscribe('signup_finalized', function (status) { // redirect or handle status 'success' / 'failure' }) ``` If you allow customers to change the total cart value, you can utilise the JS library to suspend the iframe while you perform a backen update call towards our services. As described below: 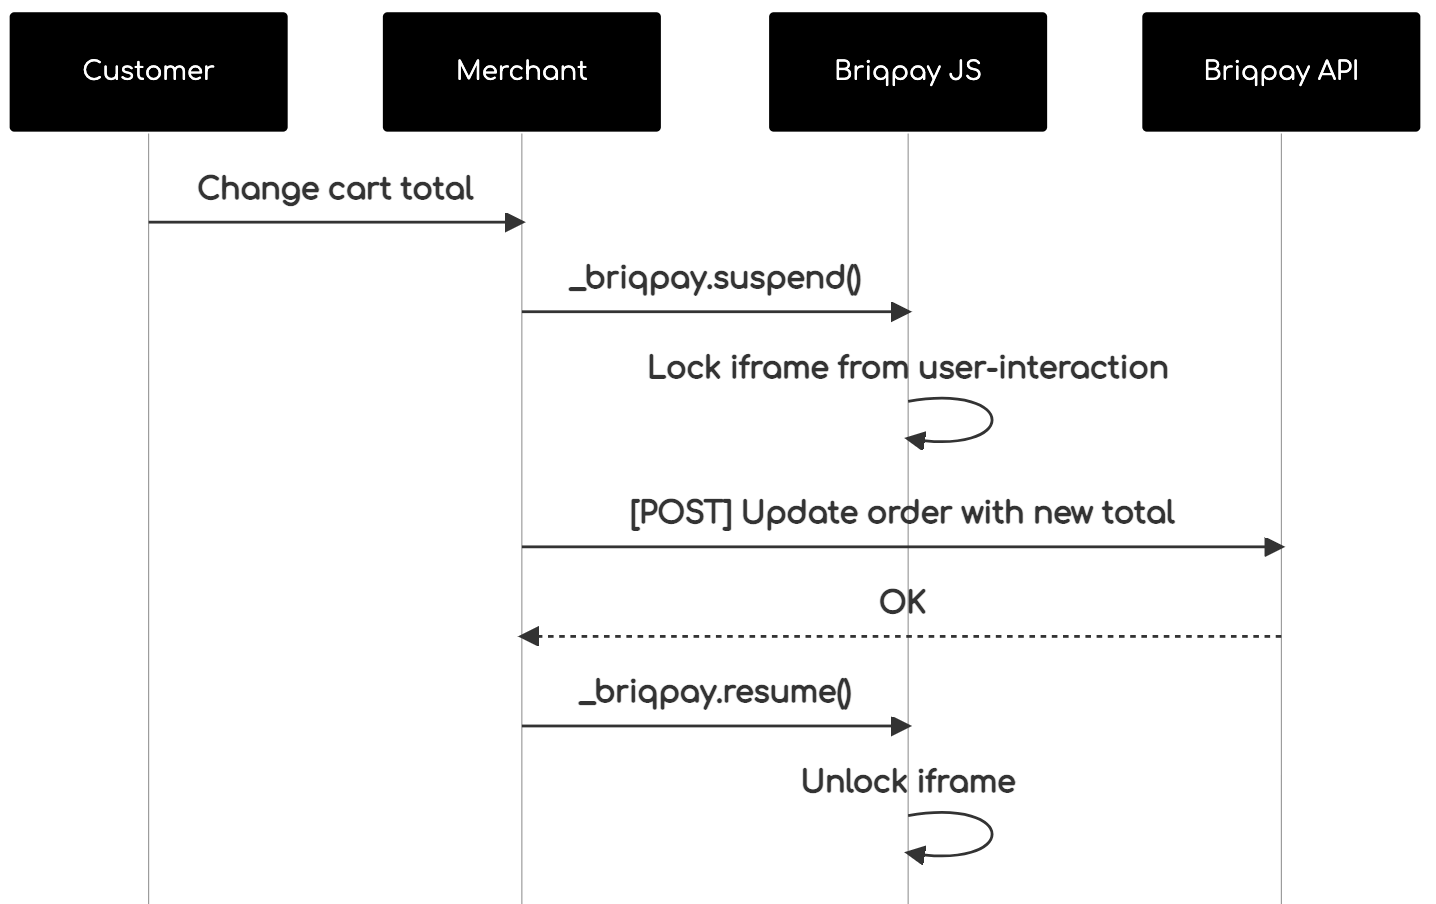 The iframe will auto-resume after 7 seconds if you dont call ``_briqpay.resume()`` before # Test Data In order to verify your integration you will neeed to use test data towards our credit engine. ## Company identication numbers * 1111111111 - To recieve a high credit scoring company ( 100 in rating) * 2222222222 - To test the enviournment with a bad credit scoring company (10 in rating) ## Card details In our playground setup your account is by default setup with a Stripe integration. In order to test out the card form you can use the below card numbers: * 4000002500003155 - To mock 3ds authentication window * 4000000000000069 Charge is declined with an expired_card code. You can use any valid expiry and CVC code # Authentication Briqpay utilizes JWT in order to authenticate calls to our platform. Authentication tokens expire after 48 hours, and at that point you can generate a new token for the given resource using the ``/auth`` endpoint. - Basic Auth - only used on the auth endpoint in order to get the Bearer Token - JWT Bearer Token - All calls towards the API utlizes this method"
localzet/core
212 Downloads
High-performance asynchronous event-driven server for PHP.
chillerlan/php-googleauth
1312 Downloads
A generator for counter- and time based 2-factor authentication codes (Google Authenticator). PHP 8.2+
naluz/framework
534 Downloads
NaluzPHP framework core: container, HTTP/PSR-15 router, ORM + query builder, NoSQL, queues, mail, scheduler, storage, templates, security.
omniauth/otp
149 Downloads
Omniauth's one-time passwords over spomky-labs/otphp, under any PHP host - authenticator applications (TOTP; HOTP possible): the second factor, its enrolment (a secret and its otpauth:// address) and its revocation, with scheb/2fa's parameters (SHA1, 30 s, 6 digits, the same leeway and provisioning address) so the secrets an application keeps today go on working, a code accepted once only, and the secrets sealed at rest with libsodium (SodiumSecretBox, the key in the host's vault; the ones kept in clear read until rewritten). Formerly omniauth/totp, which it replaces (the Omniauth\Totp\ names stay aliases for one release).
ereborcodeforge/mithrilphp
238 Downloads
MithrilPHP is a lightweight and resilient PHP engine that silently protects applications, offering a solid core runtime, console, and HTTP foundation without dictating how your domain is built.
skyyware/stage
372 Downloads
A PHP framework for people and coding agents, with explicit application boundaries.
paypaplane/svix-client
24746 Downloads
Welcome to the Svix API documentation! Useful links: [Homepage](https://www.svix.com) | [Support email](mailto:[email protected]) | [Blog](https://www.svix.com/blog/) | [Slack Community](https://www.svix.com/slack/) # Introduction This is the reference documentation and schemas for the [Svix webhook service](https://www.svix.com) API. For tutorials and other documentation please refer to [the documentation](https://docs.svix.com). ## Main concepts In Svix you have four important entities you will be interacting with: - `messages`: these are the webhooks being sent. They can have contents and a few other properties. - `application`: this is where `messages` are sent to. Usually you want to create one application for each user on your platform. - `endpoint`: endpoints are the URLs messages will be sent to. Each application can have multiple `endpoints` and each message sent to that application will be sent to all of them (unless they are not subscribed to the sent event type). - `event-type`: event types are identifiers denoting the type of the message being sent. Event types are primarily used to decide which events are sent to which endpoint. ## Authentication Get your authentication token (`AUTH_TOKEN`) from the [Svix dashboard](https://dashboard.svix.com) and use it as part of the `Authorization` header as such: `Authorization: Bearer ${AUTH_TOKEN}`. For more information on authentication, please refer to the [authentication token docs](https://docs.svix.com/api-keys). ## Code samples The code samples assume you already have the respective libraries installed and you know how to use them. For the latest information on how to do that, please refer to [the documentation](https://docs.svix.com/). ## Idempotency Svix supports [idempotency](https://en.wikipedia.org/wiki/Idempotence) for safely retrying requests without accidentally performing the same operation twice. This is useful when an API call is disrupted in transit and you do not receive a response. To perform an idempotent request, pass the idempotency key in the `Idempotency-Key` header to the request. The idempotency key should be a unique value generated by the client. You can create the key in however way you like, though we suggest using UUID v4, or any other string with enough entropy to avoid collisions. Svix's idempotency works by saving the resulting status code and body of the first request made for any given idempotency key for any successful request. Subsequent requests with the same key return the same result. Please note that idempotency is only supported for `POST` requests. ## Cross-Origin Resource Sharing This API features Cross-Origin Resource Sharing (CORS) implemented in compliance with [W3C spec](https://www.w3.org/TR/cors/). And that allows cross-domain communication from the browser. All responses have a wildcard same-origin which makes them completely public and accessible to everyone, including any code on any site.
boctulus/simplerest
75 Downloads
Lightweight PHP REST framework core. Specific libraries are distributed as separate packages.
coduo/tutu
12679 Downloads
TuTu - simple HTTP server mocking tool in PHP.
fadion/diff-match-patch
8400 Downloads
Port of the google-diff-match-patch (https://code.google.com/p/google-diff-match-patch/) lib to PHP
erikwang2013/etcd
515 Downloads
PHP etcd v3 client over HTTP (full API) and gRPC (unary RPCs), covering KV, Watch, Lease, Auth, Cluster, Maintenance, Election and Lock. Runs on plain PHP: no framework, no PSR-18 implementation and no ext-curl required. Laravel, Hyperf, ThinkPHP, Webman, Yii2 and Yii3 adapters included.
dockcodes/dock-ray
454 Downloads
PHP SDK for DockRay - application error and performance monitoring (https://dock.codes)