Libraries tagged by endpoint
fusio/adapter-v8
10880 Downloads
Write the endpoint logic in javascript using the V8 engine
evo-mark/evo-wp-rest-registration
892 Downloads
Register your Wordpress REST API endpoints easily
etracksystems/socialite-azure-app
1185 Downloads
Laravel Socialite provider for Oauth using azure, but scoped to a specific app api, allowing custom azure policies to be applied. Rather than using the MS graph endpoint which mean policies would have to be applied to that instead of the app
elgentos/m2-vatfallback-graph-ql
10626 Downloads
Provides graph ql endpoint to dutchento/m2-vatfallback
drewdan/sentinel-client
523 Downloads
Ships your Laravel application's logs to a Sentinel ingest endpoint.
devgeniem/tms-plugin-network-site-list
2181 Downloads
Provides a REST endpoint that lists the sites in a network installation.
dardangashi/filament-api-explorer
137 Downloads
An OpenAPI-driven API explorer for Filament panels: browse endpoints, inspect response schemas, copy request samples and send live GET requests.
coolms/entity-bundle
62 Downloads
Symfony integration for coolms/entity: the bundle and its extension, the extras infrastructure compiler passes, API Platform property metadata factories for dynamic fields, and the entity search endpoint
contempt/http
36 Downloads
Contempt HTTP model, compiled endpoint pipeline, FPM runtime and PSR-7/PSR-15 adapters.
concept7/laravel-forduty
296 Downloads
Point browsers at your for.duty ingest endpoint with a Reporting-Endpoints header.
codebros-nl/monitoring-client
242 Downloads
Ships Laravel application telemetry (requests, exceptions, queries, jobs, cache, scheduled tasks, outgoing requests) to the CodeBros portal's monitoring ingest endpoint, reusing Laravel Pulse's recorders for data capture.
cloudcogsio/oauth2-openid-connect-discovery
215 Downloads
This library extends the 'League OAuth2 Client' library to provide OpenID Connect Discovery support for supporting providers that expose a .well-known configuration endpoint.
chemezov/yii2-rest-api-doc
14836 Downloads
Simple documentation generator for Yii2 REST applications based on defined API endpoints and actions annotations.
cacahouwete/lazy-api-collection
4281 Downloads
Handle rest api endpoint with pagination through an unique iterable
briqpay/php-sdk
12096 Downloads
This is the API documentation for Briqpay. You can find out more about us and our offering at our website [https://briqpay.com](https://briqpay.com) In order to get credentials to the playgrund API Please register at [https://app.briqpay.com](https://app.briqpay.com) # Introduction Briqpay Checkout is an inline checkout solution for your b2b ecommerce. Briqpay Checkout gives you the flexibility of controlling your payment methods and credit rules while optimizing the UX for your customers # SDKs Briqpay offers standard SDKs to PHP and .NET based on these swagger definitions. You can download them respively or use our swagger defintitions to codegen your own versions. #### For .NET `` Install-Package Briqpay `` #### For PHP `` composer require briqpay/php-sdk `` # Standard use-case As a first step of integration you will need to create a checkout session. \n\nIn this session you provide Briqpay with the basic information necessary. In the response from briqpay you will recieve a htmlsnippet that is to be inserted into your frontend. The snippet provided by briqpay will render an iframe where the user will complete the purchase. Once completed, briqpay will redirect the customer to a confirmation page that you have defined. 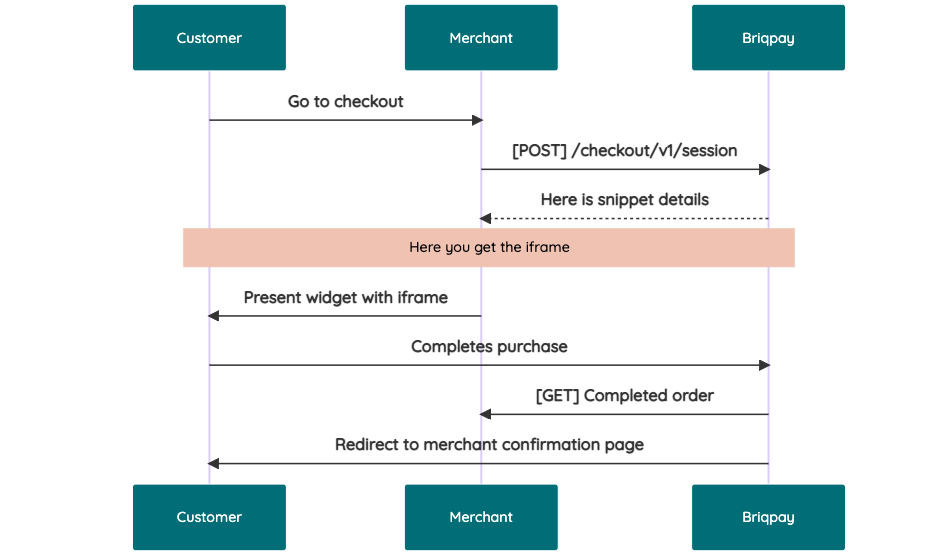 # JavaScript SDK The first step of integration is to add our JS to your site just before closing the ```` tag. This ensures that our JS library is avaliable to load the checkout. ```` Briqpay offers a few methods avaliable through our Javascript SDK. The library is added by our iframe and is avalable on ``window._briqpay`` If you offer the posibility to update the cart or order amonts on the checkout page, the JS library will help you. If your store charges the customer different costs and fees depening on their shipping location, you can listen to the ``addressupdate``event in order to re-calculate the total cost. ```javascript window._briqpay.subscribe('addressupdate', function (data) { console.log(data) }) ``` If your frontend needs to perform an action whe the signup has completed, listen to the ``signup_finalized`` event. ```javascript window._briqpay.subscribe('signup_finalized', function (status) { // redirect or handle status 'success' / 'failure' }) ``` If you allow customers to change the total cart value, you can utilise the JS library to suspend the iframe while you perform a backen update call towards our services. As described below: 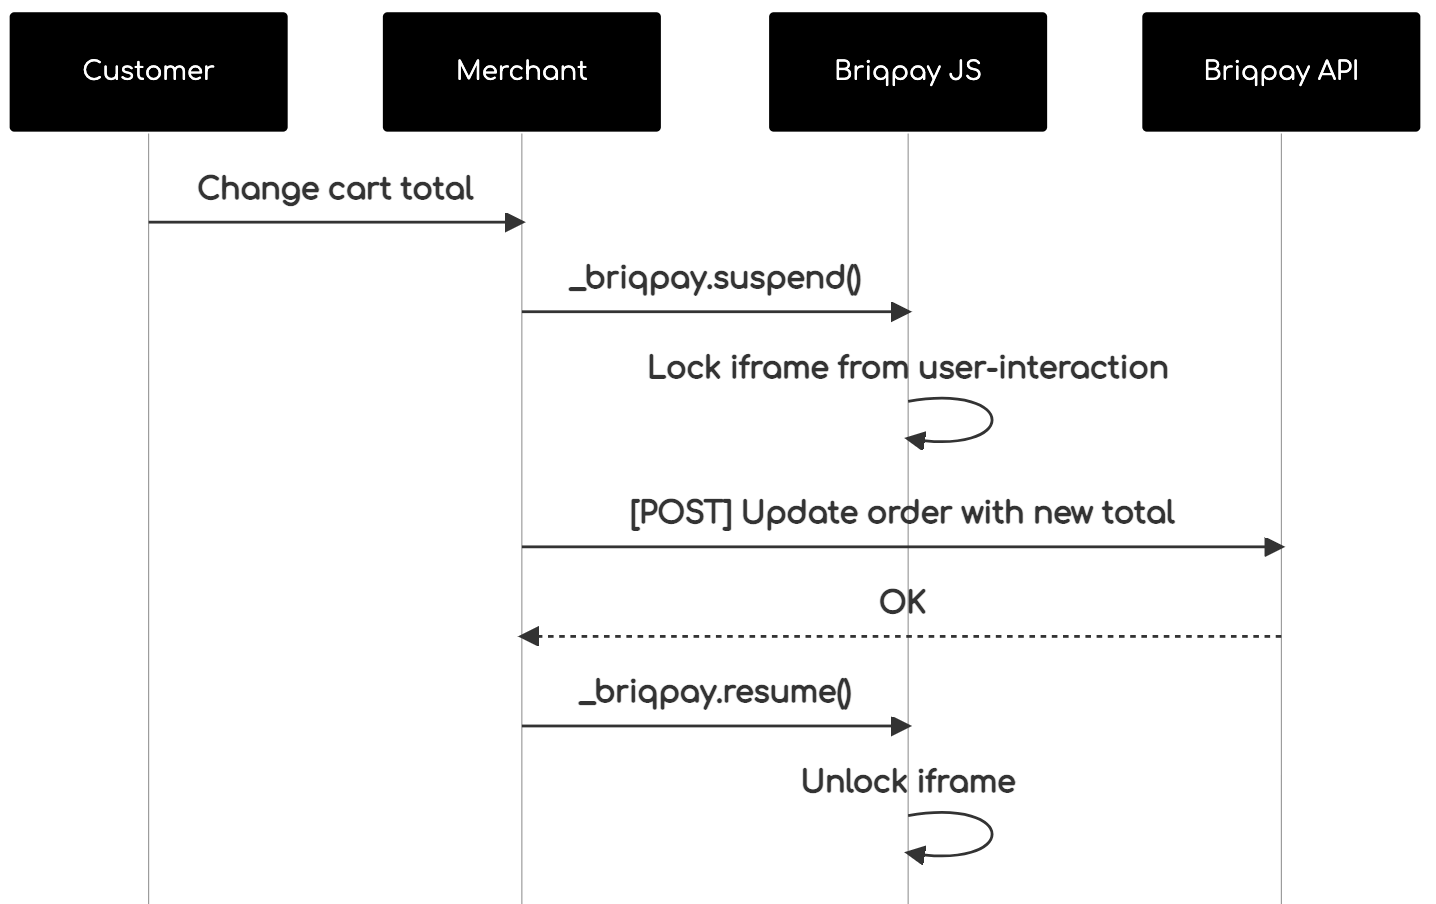 The iframe will auto-resume after 7 seconds if you dont call ``_briqpay.resume()`` before # Test Data In order to verify your integration you will neeed to use test data towards our credit engine. ## Company identication numbers * 1111111111 - To recieve a high credit scoring company ( 100 in rating) * 2222222222 - To test the enviournment with a bad credit scoring company (10 in rating) ## Card details In our playground setup your account is by default setup with a Stripe integration. In order to test out the card form you can use the below card numbers: * 4000002500003155 - To mock 3ds authentication window * 4000000000000069 Charge is declined with an expired_card code. You can use any valid expiry and CVC code # Authentication Briqpay utilizes JWT in order to authenticate calls to our platform. Authentication tokens expire after 48 hours, and at that point you can generate a new token for the given resource using the ``/auth`` endpoint. - Basic Auth - only used on the auth endpoint in order to get the Bearer Token - JWT Bearer Token - All calls towards the API utlizes this method"