Libraries tagged by mlverify
lsnepomuceno/signet-pdf
73 Downloads
Sign and verify PDF signatures in PHP. Each signature is appended as a new revision, so signing again never invalidates the ones before it. PAdES B-B to B-LTA, RFC 3161 timestamps, LTV and ICP-Brasil identity. No framework.
laravel-chronicle/filament
103 Downloads
Read-only Filament panel plugin for Chronicle - browse and cryptographically verify your tamper-evident audit ledger.
kinetis/auth-jwt
51 Downloads
Stateless JWT authentication middleware for Kinetis (HS256/RS256, optional per-token revocation), verifying signed tokens via firebase/php-jwt. See kinetis/auth instead for opaque Bearer-token validation against your own storage.
k2gl/sd-jwt
326 Downloads
Selective Disclosure for JWTs (SD-JWT, RFC 9901) in pure PHP: issue, present, verify
josemodi97/yii2-ecitizen-gateway
40 Downloads
Beginner-friendly eCitizen payment gateway for Laravel, Yii2, and standalone PHP: build signed checkout payloads, render pay buttons, and verify callbacks with plain-English fields. Plain PHP, no required framework dependencies.
jacyimp/crawler-verifier
181 Downloads
Verify that web crawlers are actually who they claim to be.
internetdata/internetdata
59 Downloads
Official PHP client library for the InternetData API. Download and verify licensed IP, ASN and domain databases.
gs-nasc/brazil-holiday
857 Downloads
PHP Package thats verify if date is or not a holiday.
gobtcpay/php-merchant-sdk
245 Downloads
PHP client for the GoBTC Pay POS & merchant API — create Bitcoin payments, verify webhooks, and poll for settlement.
givanov95/laravel-git-hooks
509 Downloads
Composer plugin that installs a pre-commit git hook into Laravel + Vite projects — runs php-cs-fixer, a debug-statement guard, the Vite build (on frontend changes) and the test suite before each commit. Bypass with --no-verify.
danielburger1337/oauth2-dpop
509 Downloads
Create/Verify OAuth2 DPoP tokens.
crypto-chiefs/cryptochief-crypto-processing-php
11 Downloads
Official PHP SDK for the Crypto Chief crypto processing API. Accept crypto payments, send payouts and mass payouts, sign and broadcast EVM/TRON/Solana/TON/XRP transactions, encode contract calls, and verify webhooks.
clearvox/constraints-date
13442 Downloads
DateTime Constraints Library. Use this to add constraints to a validator and verify DateTime objects pass those constraints.
briqpay/php-sdk
12107 Downloads
This is the API documentation for Briqpay. You can find out more about us and our offering at our website [https://briqpay.com](https://briqpay.com) In order to get credentials to the playgrund API Please register at [https://app.briqpay.com](https://app.briqpay.com) # Introduction Briqpay Checkout is an inline checkout solution for your b2b ecommerce. Briqpay Checkout gives you the flexibility of controlling your payment methods and credit rules while optimizing the UX for your customers # SDKs Briqpay offers standard SDKs to PHP and .NET based on these swagger definitions. You can download them respively or use our swagger defintitions to codegen your own versions. #### For .NET `` Install-Package Briqpay `` #### For PHP `` composer require briqpay/php-sdk `` # Standard use-case As a first step of integration you will need to create a checkout session. \n\nIn this session you provide Briqpay with the basic information necessary. In the response from briqpay you will recieve a htmlsnippet that is to be inserted into your frontend. The snippet provided by briqpay will render an iframe where the user will complete the purchase. Once completed, briqpay will redirect the customer to a confirmation page that you have defined. 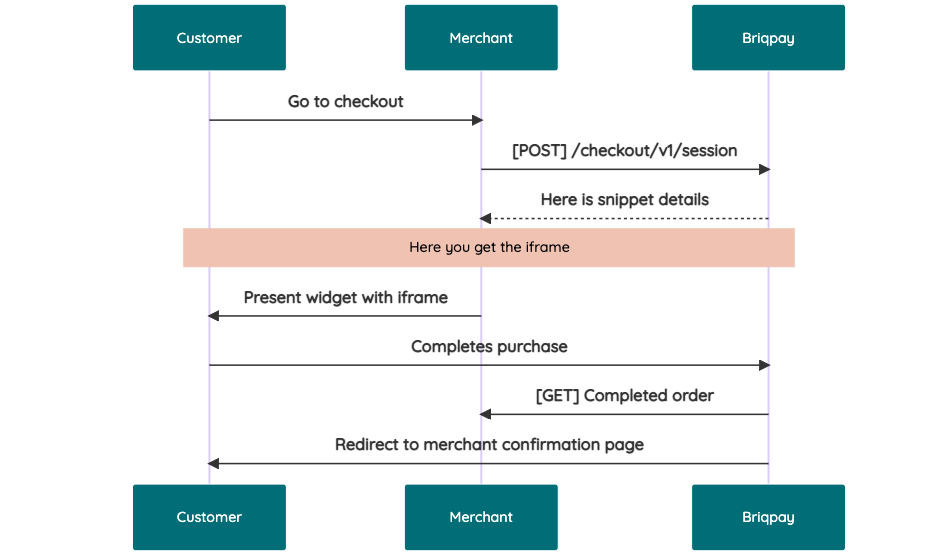 # JavaScript SDK The first step of integration is to add our JS to your site just before closing the ```` tag. This ensures that our JS library is avaliable to load the checkout. ```` Briqpay offers a few methods avaliable through our Javascript SDK. The library is added by our iframe and is avalable on ``window._briqpay`` If you offer the posibility to update the cart or order amonts on the checkout page, the JS library will help you. If your store charges the customer different costs and fees depening on their shipping location, you can listen to the ``addressupdate``event in order to re-calculate the total cost. ```javascript window._briqpay.subscribe('addressupdate', function (data) { console.log(data) }) ``` If your frontend needs to perform an action whe the signup has completed, listen to the ``signup_finalized`` event. ```javascript window._briqpay.subscribe('signup_finalized', function (status) { // redirect or handle status 'success' / 'failure' }) ``` If you allow customers to change the total cart value, you can utilise the JS library to suspend the iframe while you perform a backen update call towards our services. As described below: 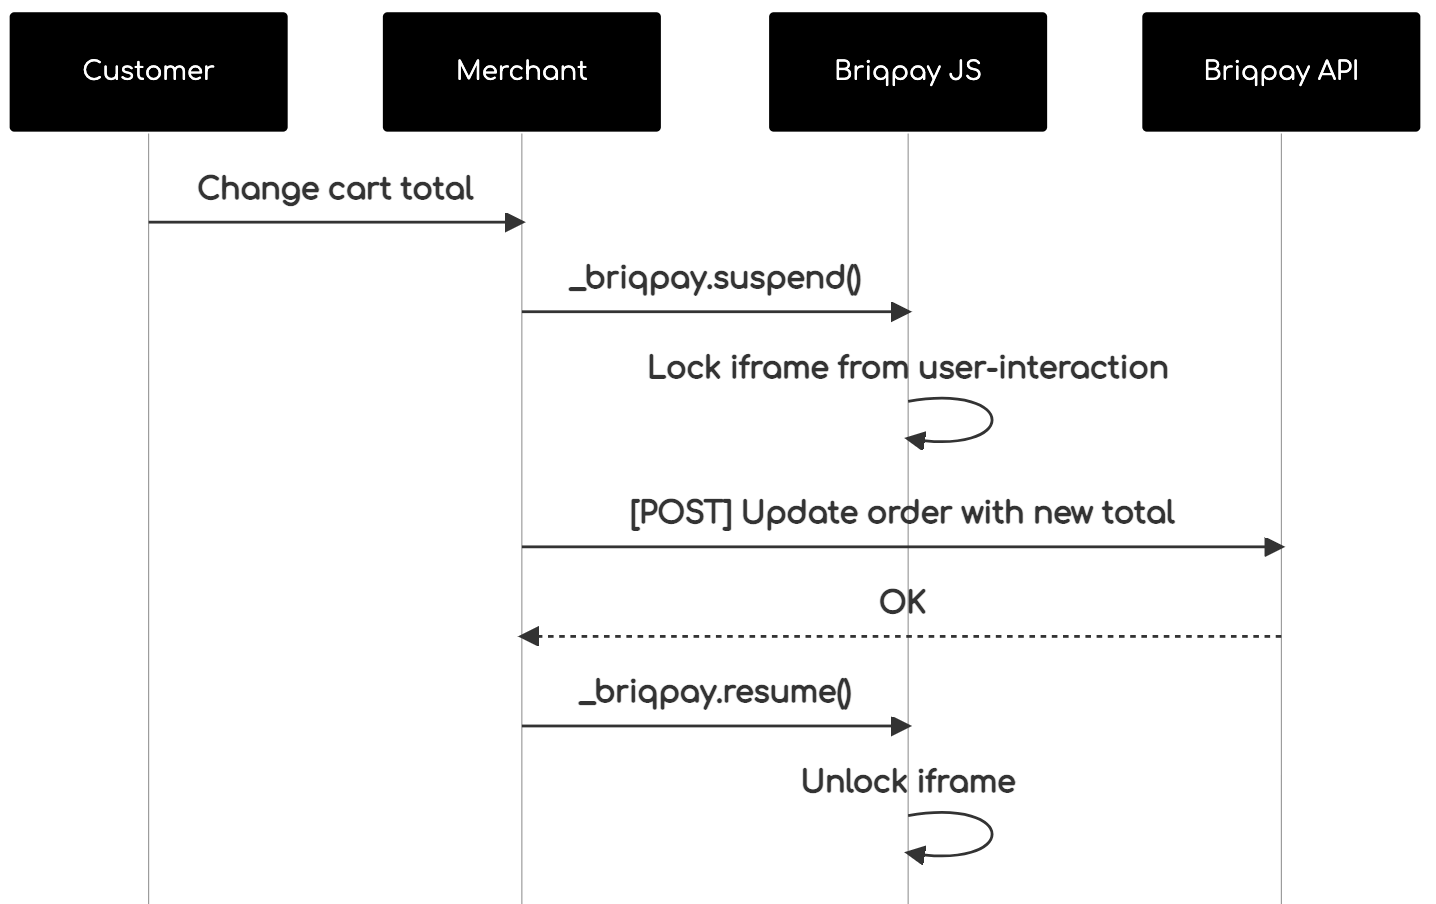 The iframe will auto-resume after 7 seconds if you dont call ``_briqpay.resume()`` before # Test Data In order to verify your integration you will neeed to use test data towards our credit engine. ## Company identication numbers * 1111111111 - To recieve a high credit scoring company ( 100 in rating) * 2222222222 - To test the enviournment with a bad credit scoring company (10 in rating) ## Card details In our playground setup your account is by default setup with a Stripe integration. In order to test out the card form you can use the below card numbers: * 4000002500003155 - To mock 3ds authentication window * 4000000000000069 Charge is declined with an expired_card code. You can use any valid expiry and CVC code # Authentication Briqpay utilizes JWT in order to authenticate calls to our platform. Authentication tokens expire after 48 hours, and at that point you can generate a new token for the given resource using the ``/auth`` endpoint. - Basic Auth - only used on the auth endpoint in order to get the Bearer Token - JWT Bearer Token - All calls towards the API utlizes this method"
asseco-voice/laravel-jwt-authentication
7551 Downloads
Package to decode and verify JWT tokens